Practical guides on NIS-2, ISO 27001, DORA, AI Act and ISO 42001 — written for compliance managers and CISOs in Europe.
What a real ISO 27001 toolkit must include, the seven checks to run before buying one, free or paid, and the red flags that predict a rough audit.
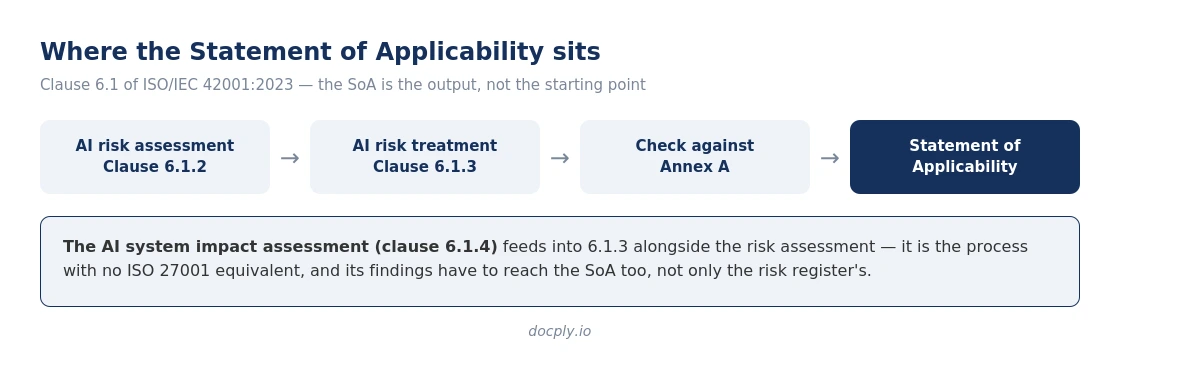
What the ISO 42001 Statement of Applicability must contain under clause 6.1.3, how to justify excluding Annex A controls, and the reasons auditors reject.
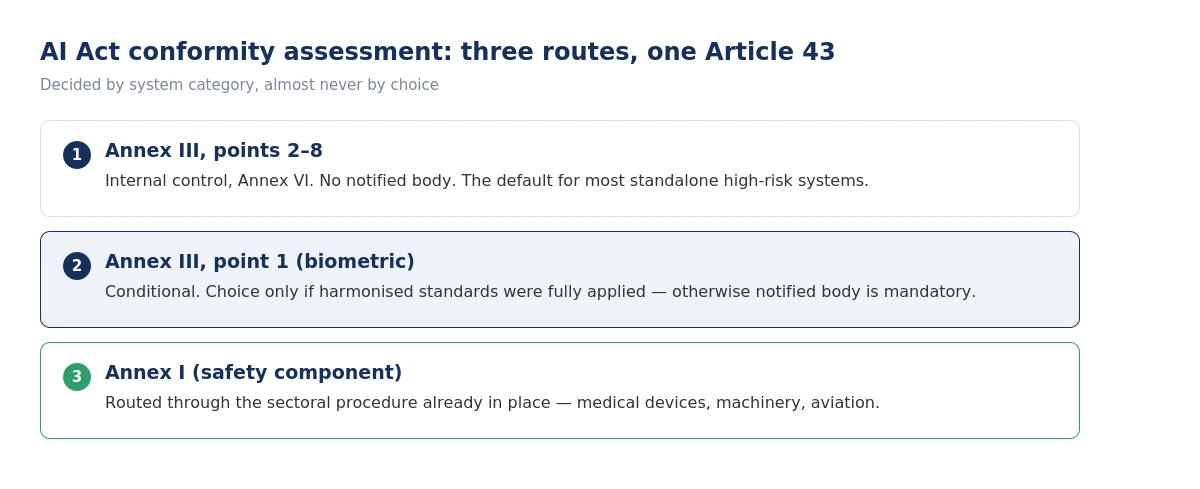
The three AI Act conformity assessment routes under Article 43, which applies to your system, what a notified body checks, and the deferred deadlines.
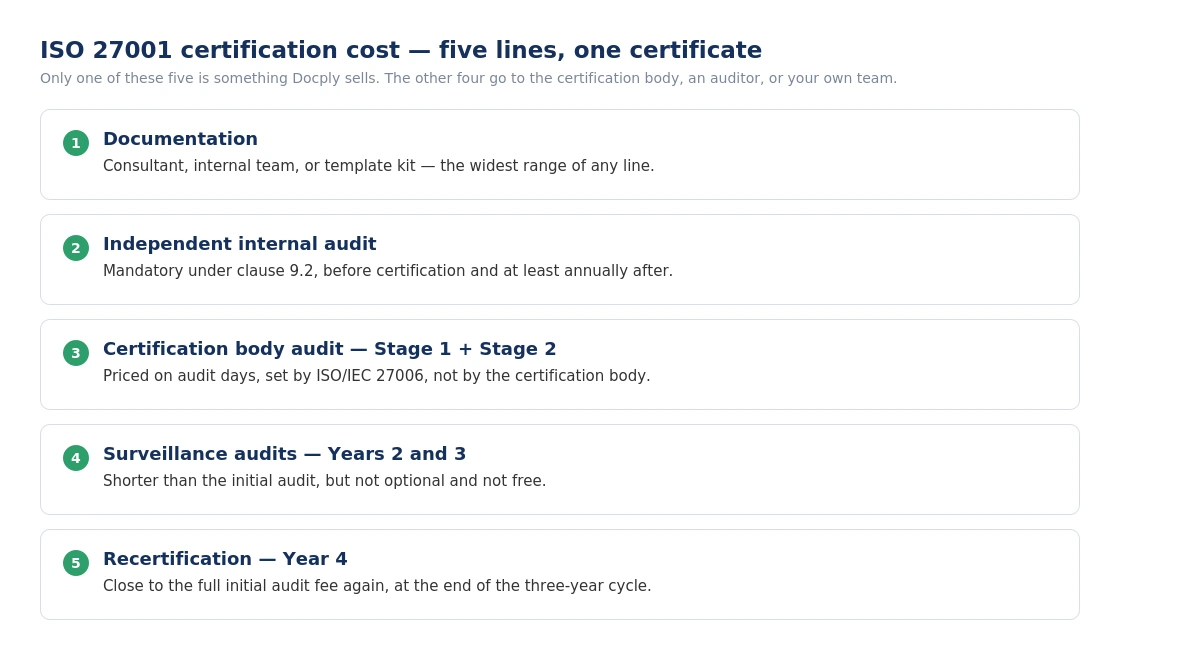
What ISO 27001 certification actually costs: audit fees, documentation, internal time, the three-year cycle, and a full worked example by company size.
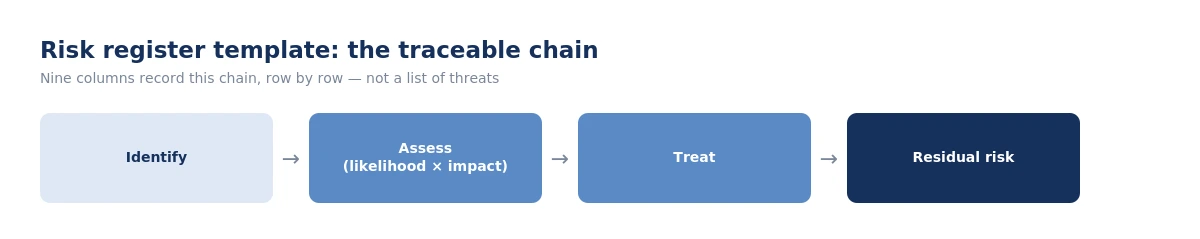
A risk register template with the columns NIS-2 and ISO 27001 auditors actually check: scoring, ownership, residual risk, treatment, and a worked example.
Most guidance on AI governance describes pillars, principles and maturity levels. This is the list of documents, registers and records that an AI management system consists of — and which ones a standard requires.
Clause 9.2 requires an impartial auditor. In a company of thirty people the only person who understands the ISMS built it. Here are the three arrangements that work and the one that fails.
Most risk assessments are built backwards from Annex A. Here is the one question that reveals it, what clause 6.1.2 actually requires, and why asset-based versus scenario-based matters less than everyone says.
Four assessments, one confusion. Where the AI impact assessment starts and your risk assessment stops, what ISO 42005 changed, and the three things that fail in an audit.
Published comparisons quote 40%, 50%, 60% overlap and none of them show the mapping. Here is what transfers clause by clause, what does not, and the claim about Annex A that is simply wrong.
You already run a quality management system and a software life cycle. Here is what an AI management system adds, what it duplicates, and where the AI Act's Annex I deadline now sits.
Regulation (EU) 2026/1744 deferred the high-risk deadlines but left the transparency duties where they were. Here is the corrected timeline and the trap in reading it as a pause.
The 2024 amendment adds one sentence to clause 4.1 and one note to 4.2. Here is what it obliges you to do, why 'not relevant' is a valid answer, and what an auditor looks for.
Most lists of mandatory ISO 27001 documents mix two different things. The standard distinguishes what must be available from what must be retained — and the distinction decides what an auditor asks you for.
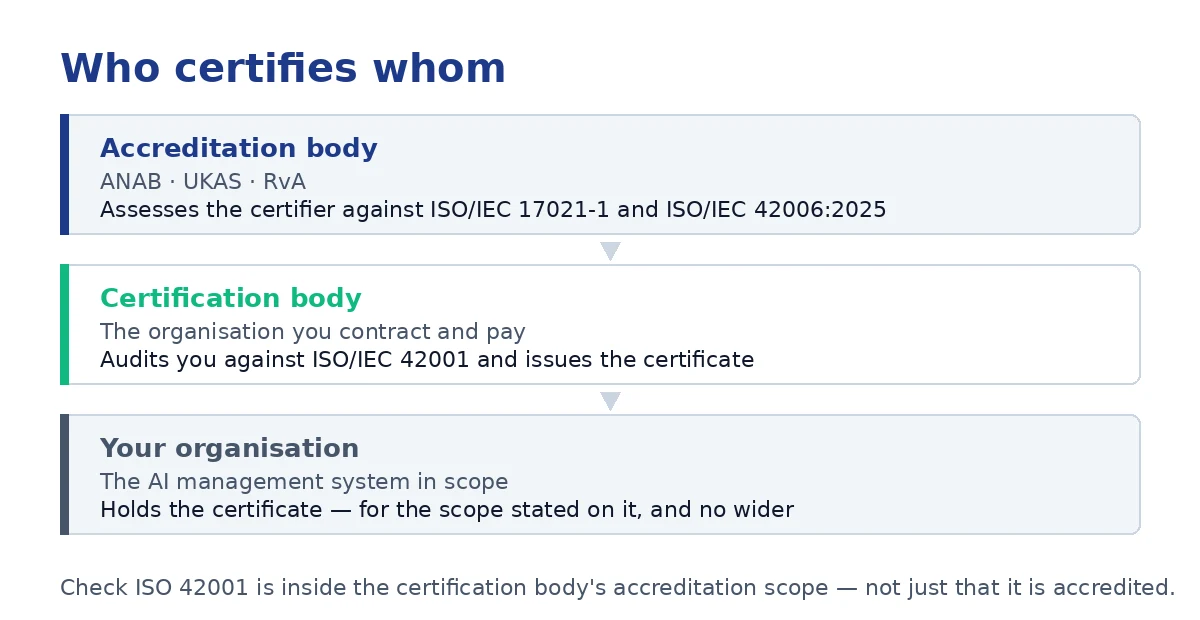
What an ISO 42001 certification audit actually involves, how to check a certification body is genuinely accredited, and the claims the certificate does not support.
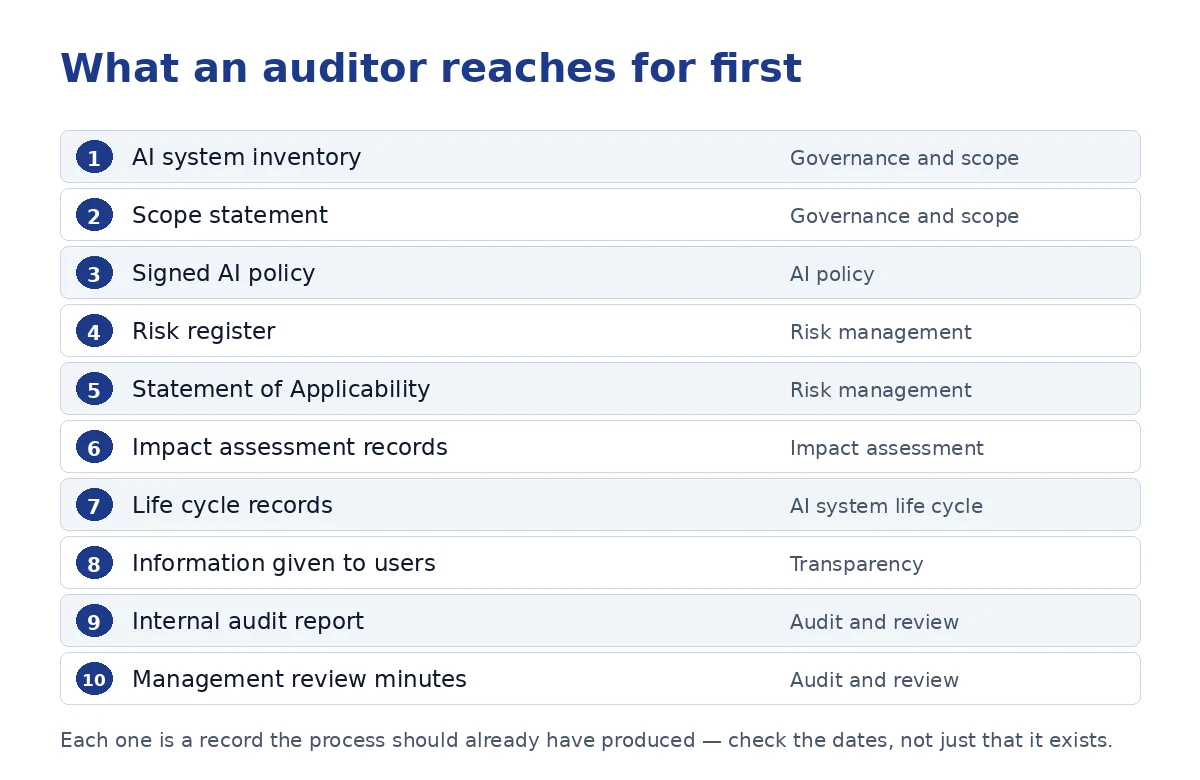
A readiness checklist for ISO/IEC 42001 organised by what produces evidence, not by clause number — the 17 documented information requirements, the 38 Annex A controls, and the records auditors sample first.
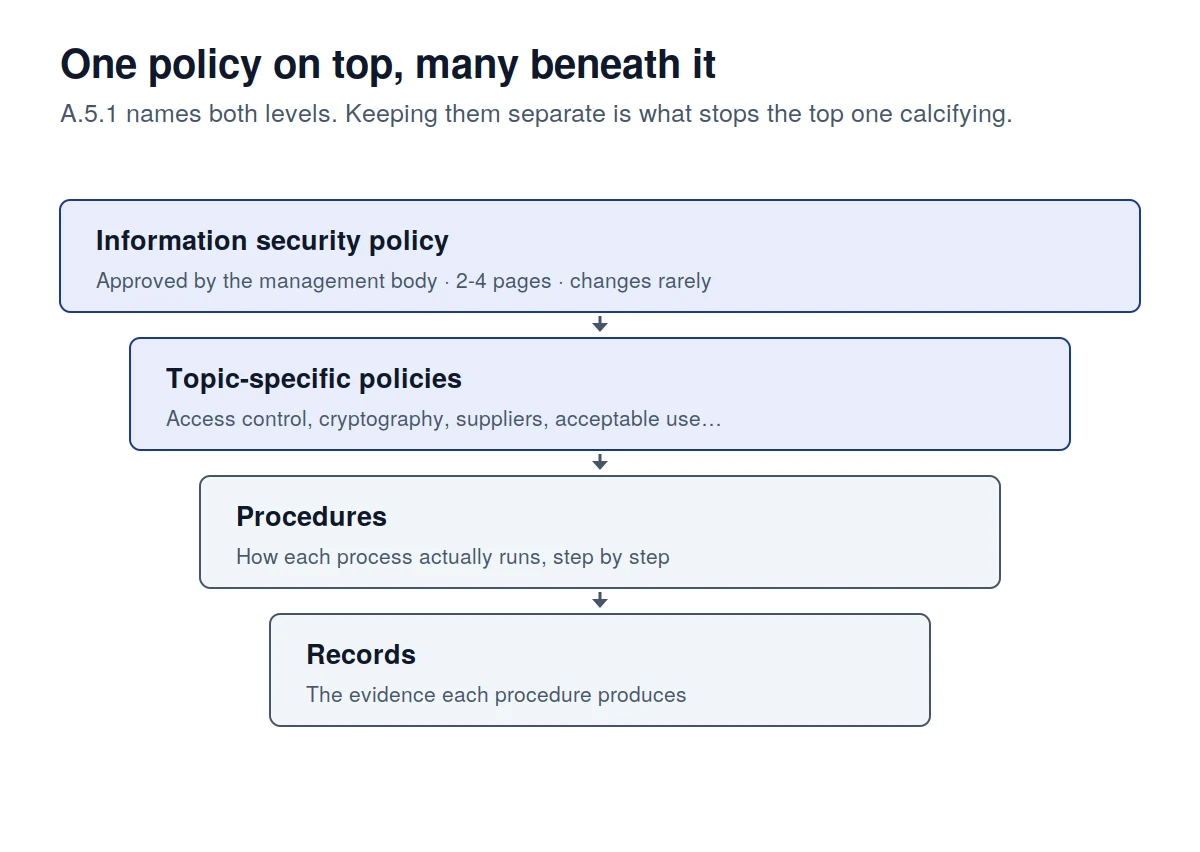
The template is the easy part. What auditors check is the approval record, the topic-specific layer beneath it, and the review trigger. Here is what belongs where.
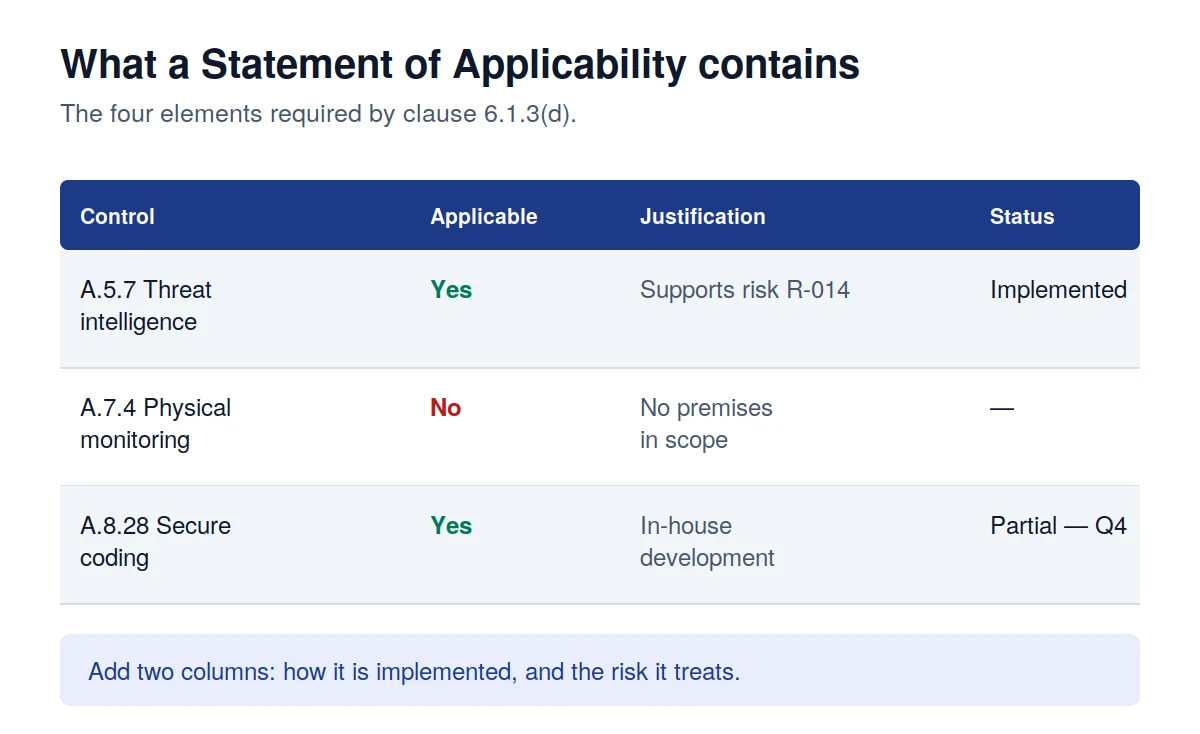
What a Statement of Applicability must contain under clause 6.1.3, how to justify exclusions, and the mistakes auditors reject. With worked rows, good and bad.
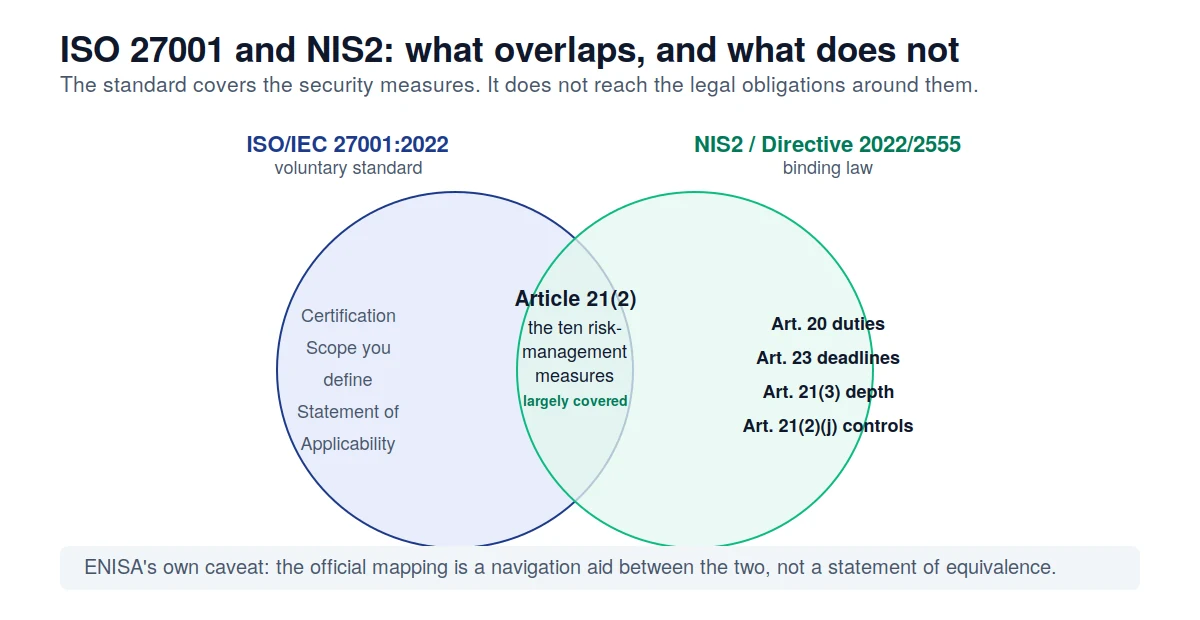
An ISO 27001 ISMS covers much of NIS2 Article 21 — but not the management body duties, the 24-hour clock, supply chain depth or MFA. The four gaps, mapped.
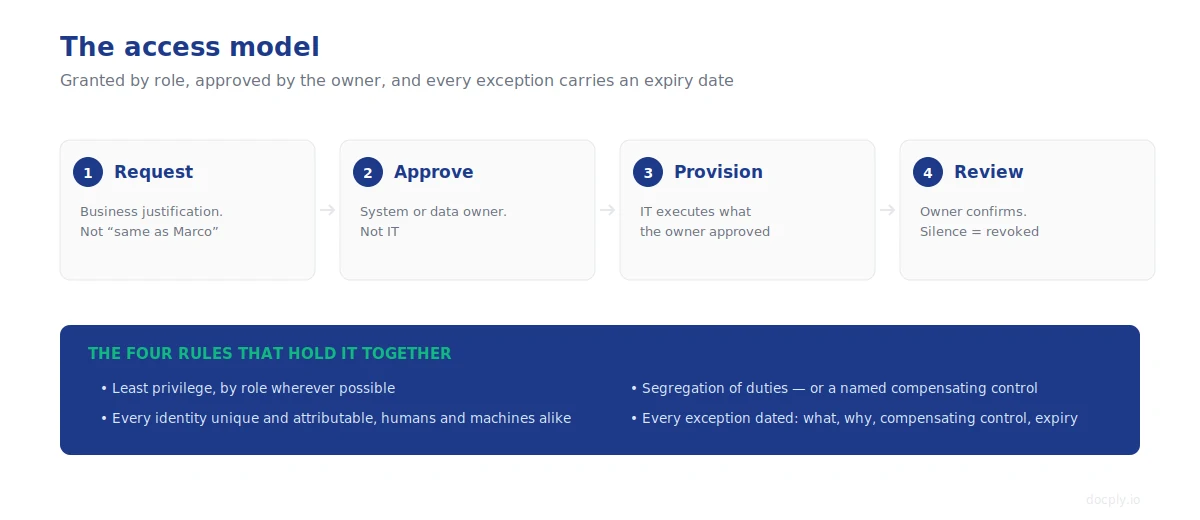
An access control policy template mapped to NIS2 Article 21(2)(i)-(j) and ISO 27001: MFA scope, privileged accounts, service accounts, same-day revocation.
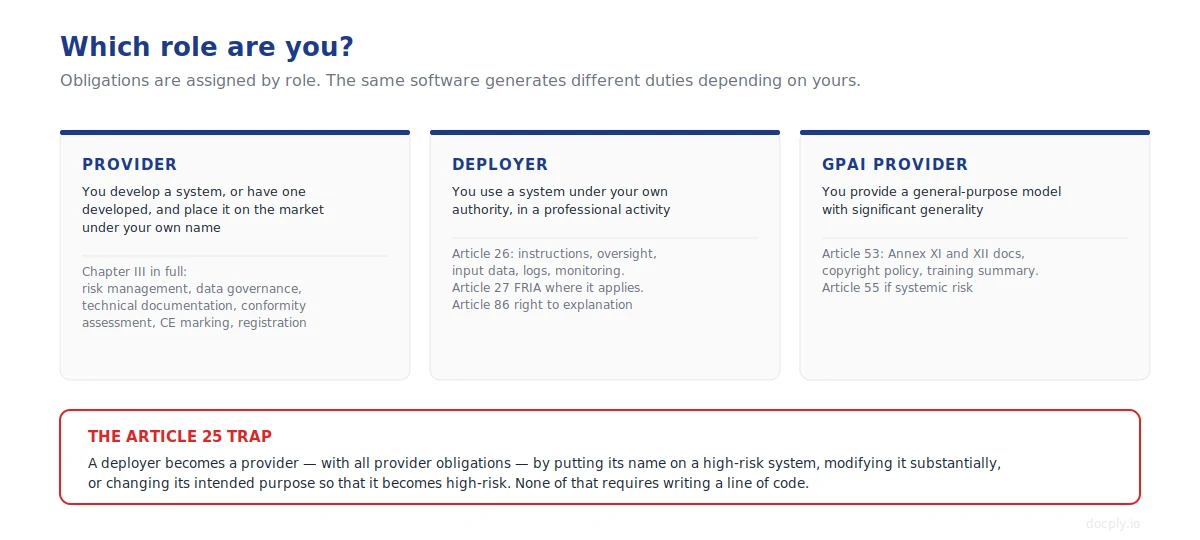
Provider, deployer or GPAI model provider? The four risk tiers, what each role owes, the application dates, and the Article 25 trap that catches deployers.
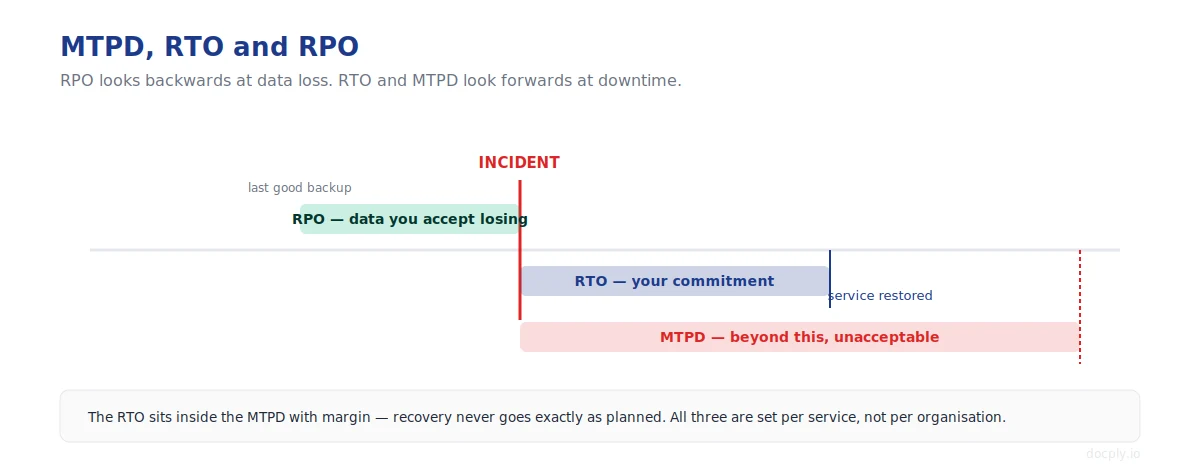
A business continuity plan template that survives use: impact analysis, RTO and RPO, recovery sequence, tested restore, crisis roles, and what NIS-2 adds.
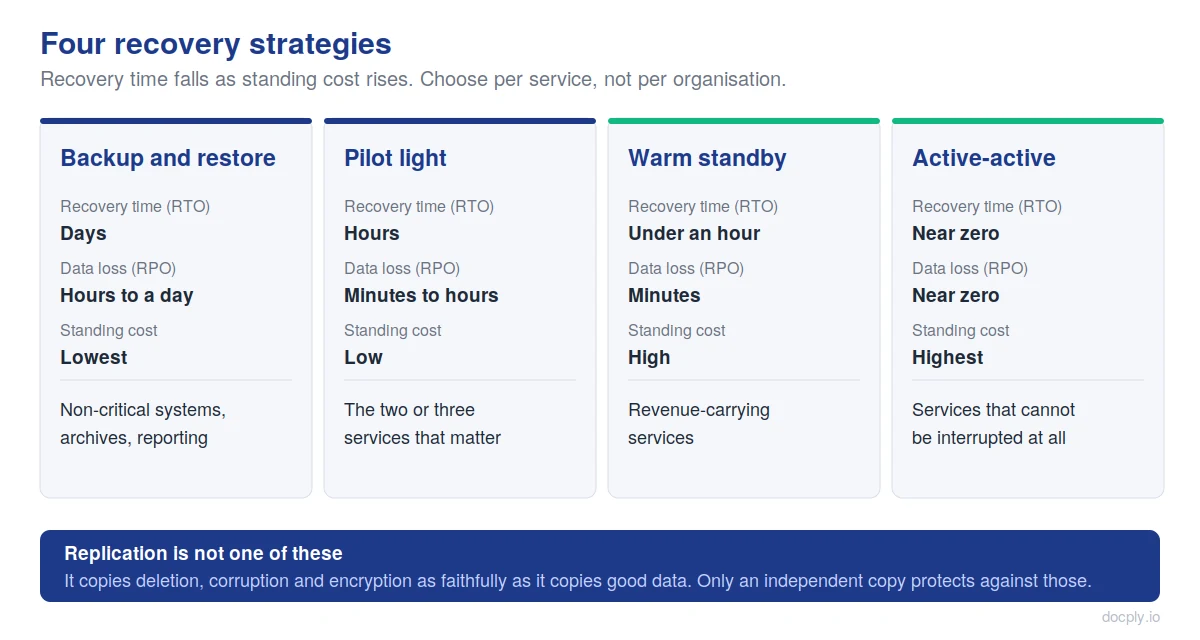
A disaster recovery plan template that works as a runbook: recovery tiers, restore order, clean recovery after ransomware, and the evidence NIS-2 wants.
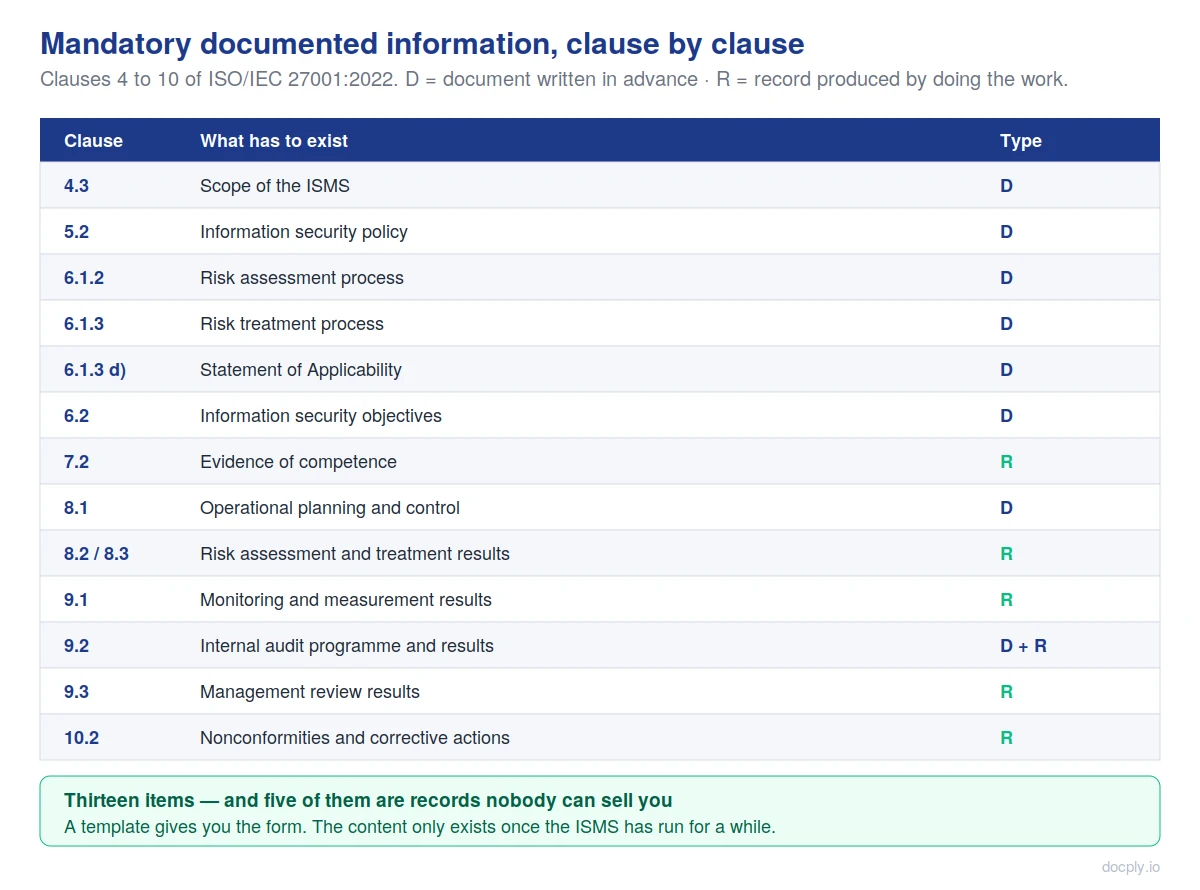
Which ISO 27001:2022 documents are mandatory, which Annex A controls imply one, what you can skip, and the errors that fail a stage 1 audit.
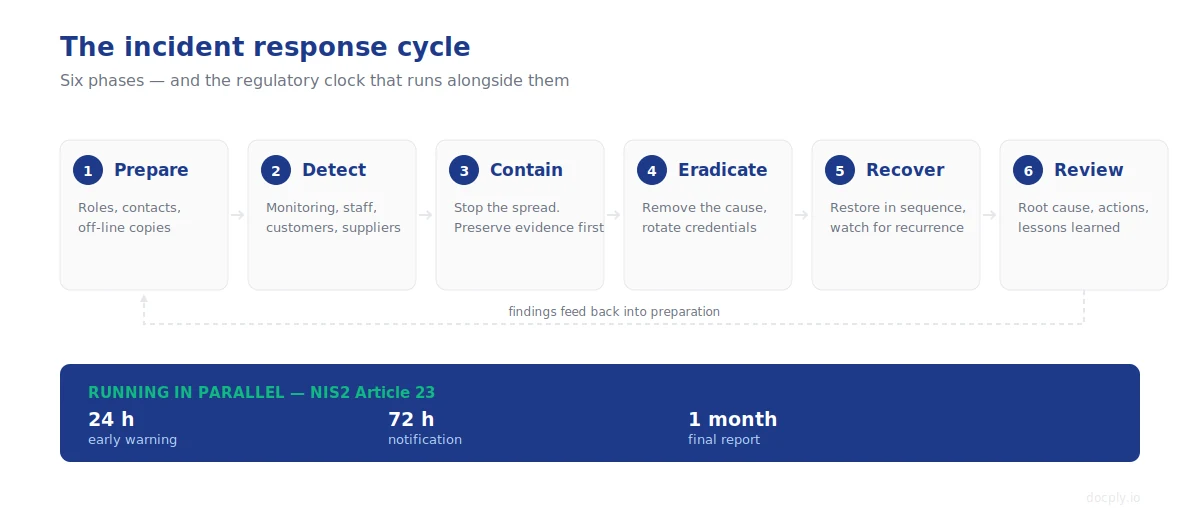
An incident response plan template built around the NIS2 24-hour reporting clock: roles, severity levels, escalation, evidence preservation, notifications.
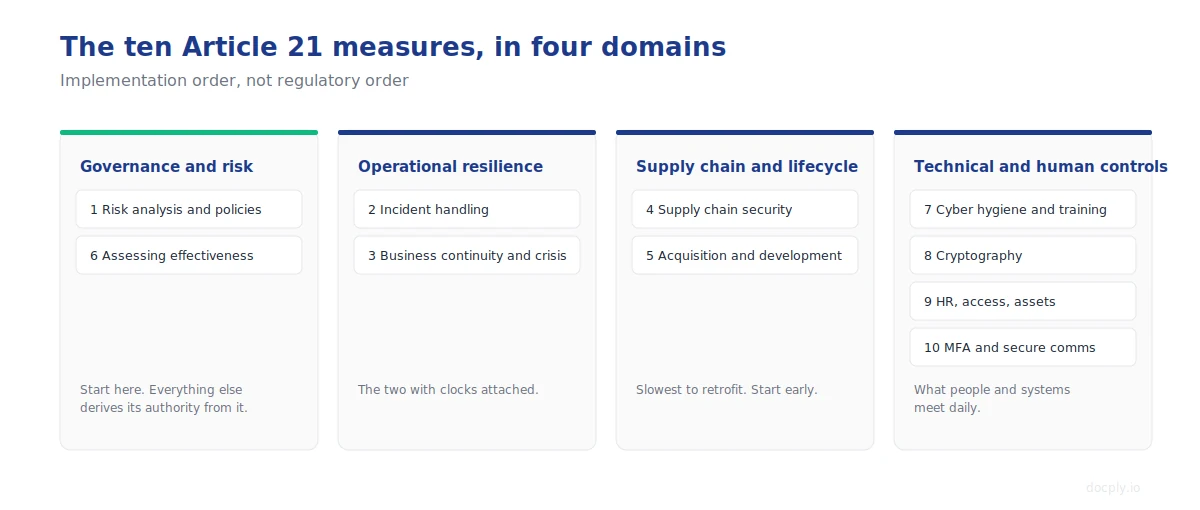
All ten NIS2 Article 21(2) requirements: what each measure needs, how it maps to Implementing Regulation 2024/2690, and the evidence regulators ask for.
Clear explanation of NIS-2 scope: which sectors and entities are classified as essential or important, and what it means for your organisation.
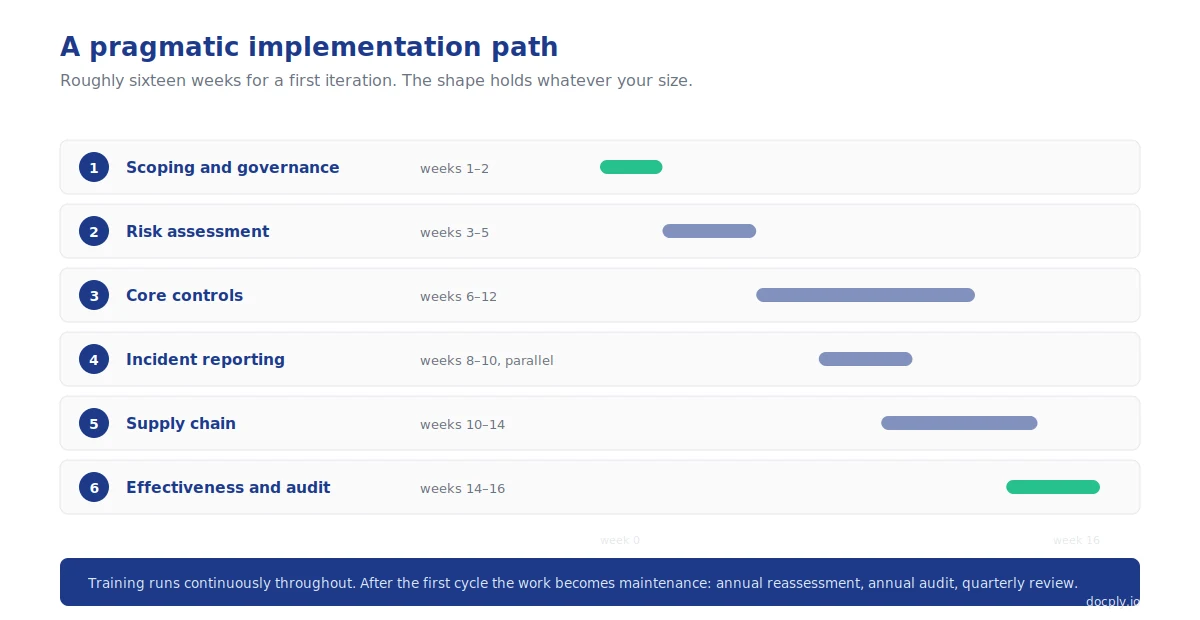
Scope, the ten Article 21 measures, the reporting clock, national deadlines and the documentation that proves it. A practical guide for 2026.