NIS-2 compliance: the complete implementation guide
2026 is the year NIS-2 stops being a paper exercise.
After a registration phase that in Italy alone brought more than thirty thousand organisations onto the national cybersecurity agency’s platform during 2025, Directive (EU) 2022/2555 has entered its operational phase across the Union. Member States have transposed it, competent authorities have published implementing measures, the first conformity assessment deadlines have already passed in some countries, and inspections are scheduled to begin in others before year-end.
The grace period is over. This guide covers what the directive requires, who it applies to, what the deadlines actually are country by country, and what documentation an inspection asks for — in the order you would build it.
In a hurry? The free NIS-2 gap assessment asks one question per obligation and scores you measure by measure — about ten minutes, and it tells you where you stand. If you would rather start from a written set, the NIS-2 Compliance Suite covers all ten Article 21 measures in thirteen procedures. €590 excl. VAT.
What NIS-2 is, and why it is not NIS-1 with a higher number
NIS-2 is a structural rewrite rather than an update. The original 2016 directive applied to roughly six thousand entities across the Union, listed “appropriate measures” without specifying which, and left enforcement to national discretion — which produced exactly the fragmented, inconsistent implementation you would expect.
NIS-2 changes four things at once. It widens scope to roughly a hundred and ten thousand entities. It mandates ten specific risk-management measures in Article 21 rather than a general obligation to be careful. It imposes a strict reporting cascade in Article 23, with deadlines measured in hours. And it makes the management body personally accountable under Article 20, with penalties that reach ten million euro or two per cent of global turnover.
The shift, in one sentence, is from “do something appropriate” to “implement these ten measures, report incidents on this clock, and prove your board approved it”.
One structural point matters more than it first appears. NIS-2 is a directive, so it does not bind organisations directly — each Member State turns it into national law, and the precise obligations, the competent authority and the registration mechanics differ by country. There is one exception, and it is worth knowing about early: Commission Implementing Regulation (EU) 2024/2690 is a regulation, applies directly and identically everywhere, and for the entity types it covers it replaces judgement with specific technical requirements. More on that below.
Who must comply
Scope is a function of three things: your sector, your size, and a handful of entity-type exceptions that override size entirely.
As a baseline, NIS-2 captures medium and large enterprises operating in one of eighteen covered sectors, split across two annexes. Medium broadly means at least fifty employees, or turnover and balance sheet above ten million euro. Micro and small organisations are generally excluded unless an exception applies.
The eighteen sectors split like this:
| Annex I — high criticality | Annex II — other critical sectors |
|---|---|
| Energy: electricity, oil, gas, hydrogen | Postal and courier services |
| Transport: air, rail, water, road | Waste management |
| Banking | Chemicals: manufacture, production, distribution |
| Financial market infrastructures | Food: production, processing, distribution |
| Health, including manufacturers of critical devices | Manufacturing: medical devices, electronics, machinery, motor and transport equipment |
| Drinking water and waste water | Digital providers: marketplaces, search engines, social platforms |
| Digital infrastructure: DNS, cloud, data centres, CDNs, trust services | Research organisations |
| ICT service management: B2B managed and security services | |
| Public administration and space |
The annex your sector sits in influences whether you are classed as essential or important. Large enterprises in Annex I sectors are essential, along with certain entity types regardless of size; medium enterprises in Annex I and medium or large enterprises in Annex II are important.
The distinction matters less than people expect. Essential entities face proactive supervision — the authority can inspect without needing a reason — while important entities are typically scrutinised after an incident or evidence of non-compliance. The security obligations themselves are identical. Only the intensity of oversight and the maximum penalties differ.
Some organisations are in scope no matter how small, because of the systemic role they play: qualified trust service providers, TLD registries and DNS providers, providers of public electronic communications, certain public administration bodies, and any entity that is the sole provider in a Member State of a service essential to societal or economic activity.
And there is a trap worth naming. Even if you are out of scope yourself, your in-scope customers must manage their supply chain risk. In practice that means they will push NIS-2-aligned requirements down to you contractually, and many smaller suppliers end up implementing the same controls anyway — through procurement rather than through law.
Our detailed guide on who must comply with NIS-2 works through the classification step by step.
The ten Article 21 measures
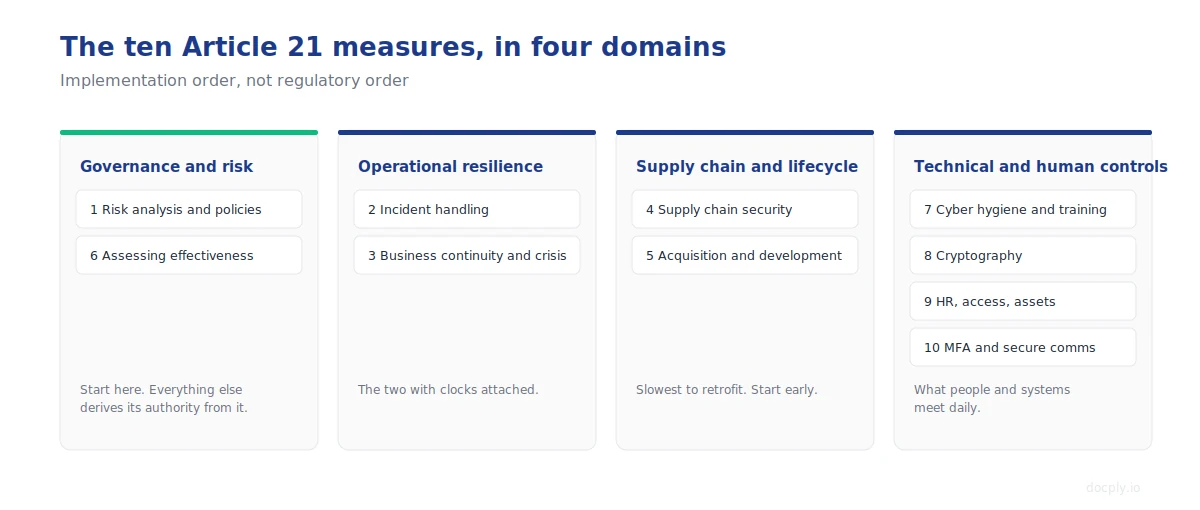 The ten measures. Proportionality governs the depth of each one, never whether you address it.
Article 21(2) requires appropriate and proportionate technical, operational and organisational measures across ten areas: risk analysis and security policies; incident handling; business continuity and crisis management; supply chain security; security in acquisition, development and maintenance; assessing the effectiveness of the measures; basic cyber hygiene and training; cryptography; human resources security, access control and asset management; and multi-factor authentication with secured communications.
Two principles govern all ten. They are technology-neutral and outcome-based, so the directive names the objective rather than the product. And proportionality applies to the depth of a measure, never to whether you address it — a small important entity might have a two-page cryptography policy where a large essential entity has ten, but both must exist.
For entities in the digital infrastructure and digital provider sectors — DNS, TLD registries, cloud, data centres, CDNs, managed and managed security service providers, marketplaces, search engines, social platforms and trust services — Commission Implementing Regulation (EU) 2024/2690 turns these ten into thirteen sections of concrete technical requirements, and its Articles 3 to 14 define when an incident is significant using measurable thresholds rather than judgement. For other sectors the regulation is not binding, but national authorities increasingly treat it as the reference for what “appropriate and proportionate” means.
Each measure, with the evidence it needs and the findings it attracts, is covered in our guide to the ten Article 21 measures.
The one part that does not vary by country
Because NIS-2 is a directive, almost everything about it is filtered through national law — which authority supervises you, how you register, what the deadlines are, what additional measures your Member State has decided to impose. That is the normal case, and it is why a compliance programme built only from the directive text will always have gaps at the national layer.
Commission Implementing Regulation (EU) 2024/2690 is the exception, and it is worth understanding even if it does not apply to you.
It is a regulation, not a directive. It applies directly and identically in every Member State, with no transposition and no national variation, to eleven entity types: DNS service providers, TLD name registries, cloud computing service providers, data centre service providers, content delivery network providers, managed service providers, managed security service providers, online marketplaces, online search engines, social networking platforms, and trust service providers.
For those entities it does two things. Its Annex turns the ten Article 21 measures into thirteen sections of specific technical and methodological requirements — considerably more prescriptive than the directive text, and much closer to something you can audit against. And its Articles 3 to 14 define when an incident is significant using measurable thresholds per entity type, replacing the judgement call that everyone else has to make.
If you are on that list, those thresholds prevail over your own assessment, and reading the Regulation alongside Article 21 is not optional. If you are not on it, the Regulation is not binding on you — but national authorities increasingly use it as the reference point for what “appropriate and proportionate” means in a sector where nothing more specific exists. Building to it is rarely wasted effort.
ENISA’s Technical Implementation Guidance maps each section of that Annex to practical measures and evidence examples, and is the most useful free document available on this subject.
The reporting clock
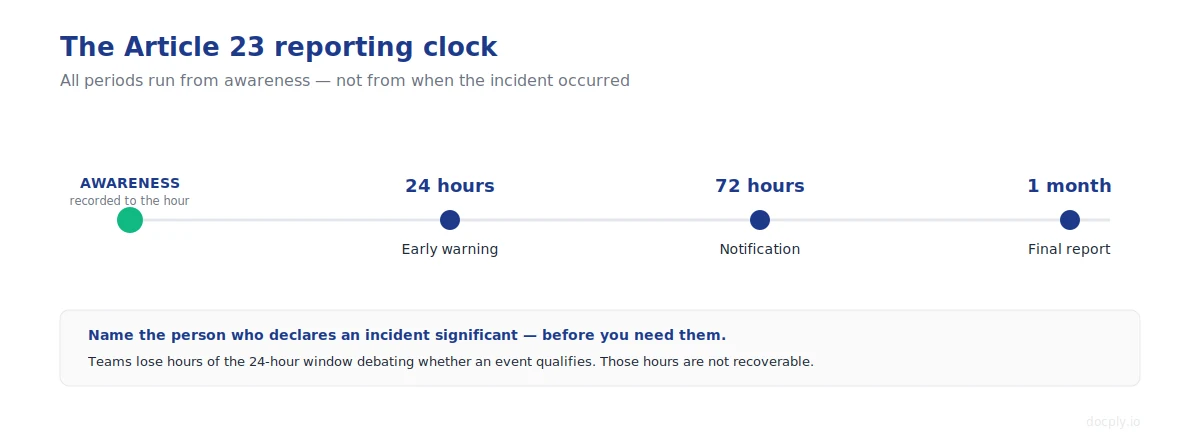 All periods run from awareness — the moment you conclude the incident is significant, recorded to the hour.
When a significant incident occurs, Article 23 starts a clock that runs whether or not anyone is watching it.
Within twenty-four hours of becoming aware, you file an early warning indicating whether the incident is suspected of being caused by unlawful or malicious acts and whether it could have cross-border impact. Within seventy-two hours, a notification updating that warning with an initial assessment of severity and impact. Within one month, a final report covering the root cause, the mitigations applied and any cross-border effect. If the incident is still open at one month, a progress report goes in instead and the final report follows once handling is complete.
Two details decide whether organisations meet these deadlines or miss them.
The first is that the clock runs from awareness, not from occurrence — the moment you conclude the incident is significant. That moment needs to be recorded to the hour, because everything else is measured from it, and reconstructing it from memory weeks later is not a position you want to be in.
The second is that teams lose hours of the twenty-four hour window debating whether an incident qualifies. The answer is to decide in advance: name the individual authorised to declare an incident significant, and name their deputy. It costs fifteen minutes now and buys back most of a day when it matters.
Filing early has a benefit beyond compliance, incidentally. Under Article 23(5) the CSIRT or competent authority must respond without undue delay, and where possible within twenty-four hours, with initial feedback and — if you ask — guidance on mitigation.
Our guide to an incident response plan that survives the 24-hour clock covers the workflow and the five submissions in detail.
The deadline calendar
Talking about “the NIS-2 deadline” is misleading, because there is no single date. There is a cascade of national deadlines that vary by Member State and by entity classification. As things stand in 2026:
| Member State | Where it stands |
|---|---|
| Italy | D.Lgs. 138/2024 in force from 16 October 2024. Registration was due by 28 February 2025. Notification obligations operational from January 2026 for the first cohort. Basic security measures due October 2026 for entities listed in 2025, and July 2027 for those first listed in 2026. ACN inspections can begin from October 2026. |
| Germany | The NIS-2 Implementation Act amended the BSI Act, in force 6 December 2025. Registration portal opened 6 January 2026, with a three-month registration window. Around 29,500 entities now under BSI supervision, up from 4,500 under NIS-1. |
| Belgium | First Member State to enforce a hard conformity assessment deadline. By 18 April 2026 essential entities had to demonstrate active implementation via CyberFundamentals verification, ISO 27001 certification with the Statement of Applicability and latest internal audit, or direct inspection. Self-attestation alone was not accepted. |
| Poland | The amended Act on the National Cybersecurity System in force 3 April 2026, with the official entity list launched 13 April. Scope expanded to roughly 42,000 organisations. |
At EU level, in January 2026 the Commission proposed targeted amendments aimed at simplifying compliance, particularly for the several thousand micro and small enterprises drawn into scope. Those amendments are still in the legislative process: nothing has changed for in-scope entities, and existing obligations remain fully applicable.
The pattern across Member States is consistent. 2025 was registration and self-classification. 2026 is implementation and the start of supervision. 2027 is full operational compliance for entities first listed in 2026.
These dates move. Confirm against your own national authority before you plan around them — the national layer is the part of NIS-2 that changes fastest.
Documentation: what an inspection asks for
The common mistake is treating NIS-2 as a control-implementation project and discovering at audit time that controls without evidence are indistinguishable from no controls at all. Article 21 is implementation; what gets inspected is evidence of implementation.
A credible documentation set covers eight areas.
Governance and setup means a scope statement, a governance model identifying roles and responsibilities, and the record of the management body approving the programme. Risk management means a methodology, a current assessment with owners assigned, and a treatment plan. Cybersecurity operations is the largest block for most organisations: access control, authentication, cryptography, secure configuration, vulnerability and patch management, logging, malware protection, network security and acceptable use.
Then business continuity and crisis management — impact analysis, continuity and recovery plans, backup policy with tested restore, crisis communication. Supply chain security — supplier policy, risk register, contractual clauses, monitoring. Effectiveness and audit — audit programme, reports, indicators, management review records, corrective actions. Incident management — response plan, handling procedure, the Article 23 submission templates, incident register. And training — a plan that includes the management body, with completion records.
What “evidence” means in practice
The word does a lot of work in this directive, and it is worth being concrete about it.
Evidence is not the policy. It is the record the policy produces when someone follows it. An access control policy is a statement of intent; the access review record signed by the system owner in March is evidence. A business continuity plan is a document; the restore test report saying you recovered service in four hours and twenty minutes against an objective of four hours is evidence — and the fact that you missed the objective by twenty minutes is far better evidence of a working system than a plan claiming you would have made it.
This is why the effectiveness measure, Article 21(2)(f), matters more than its position in the list suggests. It is the measure that produces the evidence for all the others.
Three practical tests, applied to any document in your set. Does it name someone accountable, rather than a department? Does following it produce a dated record somewhere? And has anyone actually looked at that record since it was created? A document that fails all three is not a control, whatever its title says.
The exact document count matters less than coherence. A smaller set that is approved, current, used and demonstrably reviewed beats a thicker set that lives in a folder nobody opens — and more documents is not the same as more coverage. What matters is that every obligation maps to something that exists, has an owner, produces a record and gets reviewed.
Penalties and personal liability
NIS-2 introduces a harmonised penalty regime that NIS-1 lacked. Essential entities face administrative fines of at least ten million euro or two per cent of total worldwide annual turnover, whichever is higher; for important entities the ceiling is seven million or 1.4 per cent.
The fines are the headline, but the operational consequences often bite harder. Authorities can issue binding instructions, order you to inform affected customers of a threat, require remediation within a deadline, and publicise the breach. For essential entities that fail to act, they can go further — temporarily suspending a relevant certification or authorisation, and temporarily prohibiting individuals at management level from exercising managerial functions.
Worth knowing how the ceilings are actually applied: Article 34 sets the maximums, but Member States legislate the exact amounts and the calculation method within them, so what you face varies by country. The figures above are the EU-level floor for what national regimes must allow, not a prediction of any particular fine.
In practice, the first enforcement actions across Member States have tended not to be about sophisticated security failures. They have been about registration deadlines missed, notifications filed late, and organisations unable to produce a management body approval record when asked. Those are administrative failures, they are the cheapest to avoid, and they are the ones authorities can establish without a technical investigation.
That last power is what makes NIS-2 land in the boardroom rather than the server room. Our guide to the ten Article 21 measures covers the supervisory toolkit, the penalty regime and the management-body duties in detail.
A pragmatic implementation path
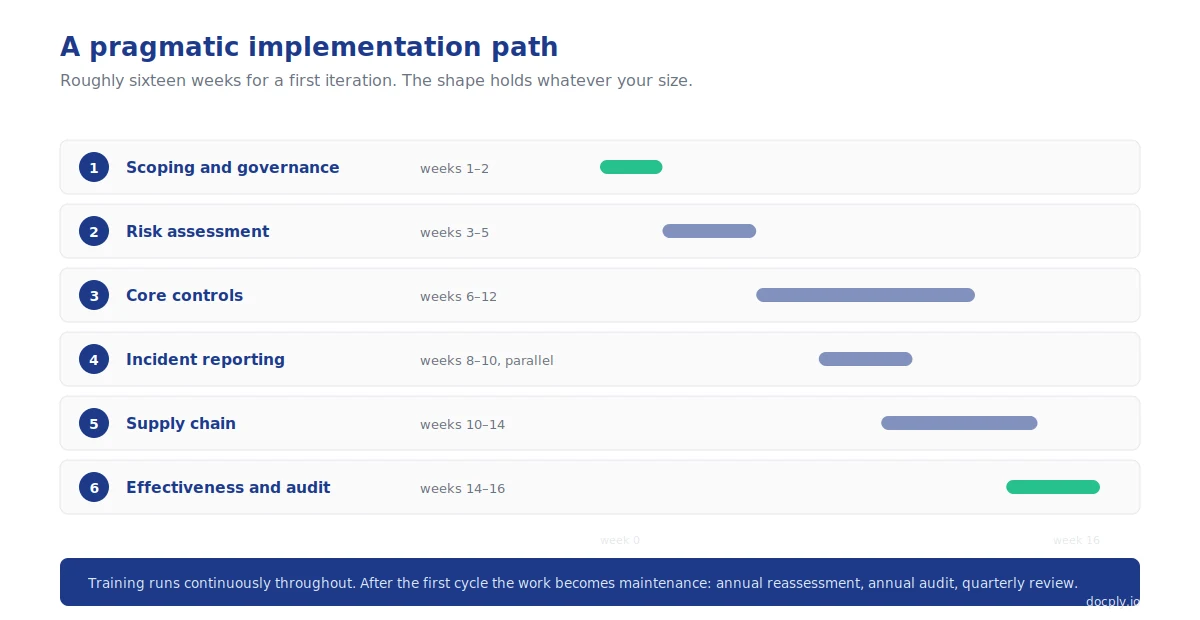 A first iteration of roughly sixteen weeks. The shape holds whatever your size; only the duration changes.
Compliance projects fail when they try to do everything at once. NIS-2 is broad enough that the only way through is in stages, each producing evidence the next can build on.
Start with scoping and governance, in the first two weeks. Confirm whether you are essential, important or out of scope, register on the national platform if applicable, define who owns what and how escalation works, and schedule the first management body training.
Weeks three to five are the risk assessment. Inventory your critical assets, services and data, apply a documented methodology, and produce the register and treatment plan with owners and timelines. Get the management body to approve both — that approval is the first substantial piece of Article 20 evidence in your file.
From week six to twelve, implement the core controls in priority order: governance and access control first, then incident handling and continuity, then supply chain. Document what already exists and implement what is missing. Resist writing policies for controls that are not actually operating, because that gap is visible to an auditor within minutes.
Running in parallel from about week eight, build the incident reporting capability: detection, classification, and the pipeline that produces the Article 23 submissions. Define what counts as significant, name the decision-makers, and test the workflow with a tabletop before you need it for real.
Supply chain work occupies weeks ten to fourteen and is the slowest to retrofit, which is why it should not be last in practice even though it often is. Inventory your direct suppliers, assess the critical ones, get security clauses into new contracts and renegotiate the critical existing ones.
Weeks fourteen to sixteen close the loop: the first internal audit, documented findings and corrective actions, and the first management review. This stage is what turns implementation into a system — without it the programme drifts within months.
Training runs continuously throughout, role-based, with completion tracked.
After the first cycle the work becomes maintenance: annual risk reassessment, annual internal audit, quarterly management review, continuous incident handling and supplier monitoring.
Four things to do this week
If you are starting from close to zero, these four give the most back for the least effort, and none of them requires the programme to exist first.
Confirm your classification and register if you have not. Late registration is among the easiest failures to be penalised for and among the hardest to argue against.
Name the person authorised to declare an incident significant, and their deputy, and tell them. Fifteen minutes, and it protects the deadline you are most likely to miss.
Find out when your last restore test was. If the answer is “we have backups” rather than a date and a duration, book one.
Brief the management body — sixty to ninety minutes on what NIS-2 obliges, what their personal exposure is, and what they need to approve. Then document the briefing, because it is the first piece of evidence in the Article 20 file.
Frequently asked questions
What is the difference between NIS-2 and NIS-1? NIS-1 applied to roughly six thousand entities, listed “appropriate measures” without specifying them, and left enforcement to national discretion. NIS-2 covers around a hundred and ten thousand entities, mandates ten specific measures, imposes the 24/72-hour reporting cascade, makes the management body personally accountable, and harmonises penalties. It is a rewrite, not an update.
Does NIS-2 apply to companies outside the EU? It can. Entities established outside the Union that provide covered services within it may fall in scope, and some categories are required to designate a representative in the Union. The test is where the service is provided, not only where the company is registered.
Is ISO 27001 enough for NIS-2? It covers a large share of Article 21 and is the fastest route if you already hold it. Four gaps are consistent: supply chain depth under Article 21(3), management body accountability under Article 20, the Article 23 reporting deadlines, and the explicit MFA expectation. ISO 27001 is one way to demonstrate compliance, not a legal substitute.
How long does implementation take? A first iteration of fourteen to sixteen weeks is realistic for a mid-market organisation with reasonable IT maturity. Larger and more complex organisations take longer. The documentation footprint alone takes weeks to build, not days, which is why starting late is expensive.
What happens if we miss a reporting deadline? Missing it is itself a compliance failure, independent of how well the incident was handled technically. Authorities can issue binding instructions, require remediation and impose administrative fines.
Do we need to register even if we think we are out of scope? If your national regime operates a registration platform, the safest position is to check the classification criteria formally and record the conclusion, whether or not you register. An undocumented decision that you were out of scope is difficult to defend later, and self-classification errors are among the most common enforcement triggers.
What counts as a significant incident? An incident that has caused or is capable of causing severe operational disruption of your services or financial loss to you, or that has affected others by causing considerable material or non-material damage. “Capable of causing” matters: an incident contained before it disrupted anything can still be significant. For the eleven entity types covered by the Implementing Regulation, specific numeric thresholds apply instead.
Who in the organisation should own NIS-2? Operationally, whoever owns information security. Accountably, the management body — Article 20 does not allow that to be delegated away. In practice the workable arrangement is a named project lead who prepares the evidence and a named member of the management body who approves it and answers for it.
How much of this can be outsourced? The implementation work can largely be outsourced; the accountability cannot. A managed service provider can run your detection and response, but the obligation to report within twenty-four hours remains yours, and so does the obligation to have assessed that provider as a supplier under Article 21(2)(d).
Where to go next
If you are aligning to ISO 27001 alongside NIS-2, note that the standard was amended in 2024: clause 4.1 now requires a climate change determination, recorded even when the conclusion is that it is not relevant.
The free NIS-2 gap assessment asks twelve questions, one per obligation, and scores you measure by measure. Ten minutes, and it produces the list of what you could not evidence today if someone asked.
If you would rather start from a complete written set, the NIS-2 Compliance Suite covers all ten measures in thirteen procedures — one per process, each opening with a table mapping every obligation to the step that discharges it, the role accountable and the record it produces. Everything that varies by Member State lives in a single annex you complete once, so the same kit works in any EU country. €590 excl. VAT.
The rest of the NIS-2 cluster goes deeper on each piece: the ten Article 21 measures, who must comply, and building an incident response plan.
Sources
Directive (EU) 2022/2555 and Commission Implementing Regulation (EU) 2024/2690 are available on EUR-Lex. ENISA’s Technical Implementation Guidance maps the Implementing Regulation Annex to practical measures with evidence examples.